How to Activate on CDP Data: Combine Your CDP and Personalization Technology

This article was written by Andy Zimmerman, Chief Marketing Officer for Evergage.

Personalization is a top investment priority for retailers in 2019, according to a recent Forrester report. And McKinsey says that “personalization will be the prime driver of marketing success within five years.” It’s clearly something that retailers can’t afford to ignore.

In order to personalize an experience, you need a good understanding of who that person is. In other words, you need to be able to collect and interpret customer data. 

You’re already collecting data about each customer and prospect across interactions and channels: in your store, on your website or mobile app, with your emails, via social media, through your advertising, and more. Each interaction produces data — data that can be used to better understand that person’s needs and preferences. 

But this data can’t be used successfully when it’s scattered across your organization. That’s where the customer data platform (CDP) comes in. Within a CDP, each person, whether known or anonymous, has a single profile that contains all relevant data from a variety of sources including purchases, browsing history, email interactions, attributes, subscriptions, loyalty membership and status, interests and preferences, browser type, location, demographics, predictive scores (like expected life-time value), and more.

Most retailers have already heard of the emerging CDP category, so I’m not going to get into the details of what CDPs are. Instead, I want to focus on what to do with your CDP data once you have it all together.

What to do with a CDP: Activation

In order to personalize using data from a CDP, you have to be able to activate it. Activation of CDP data can take many forms. For example, you could use CDP data to:

  • Determine which promotions or offers to target to each person based on his or her past behaviors, interests, loyalty program status, etc.
  • Deliver digital ads only to people most likely to be affected by them — and avoid spending money advertising to loyal customers who are more likely to purchase on their own.   
  • Ensure web and email CTAs are always relevant to the recipient (for example, removing/changing CTAs for actions a person has already taken).
  • Recommend content, products, brands, and more based on everything that is known about that person – in the moment and over time.

Many retailers view the ability to act on customer data to deliver personalized experiences as functionality that should exist outside the CDP. But I disagree. It belongs within the CDP itself.

How to Activate Efficiently: Combine CDP and personalization

Delivering these kinds of personalized experiences requires two types of functionality: insights and engagement. Often, these functions are performed by two systems.

  • System of insight: Aggregates customer/prospect data and enables an analysis of that data.
  • System of engagement: Delivers experiences to customers/prospects in one or more channels and enables measurement of the outcome.

However, having two platforms – one for insights and one for engagement – effectively creates a technology environment with two “brains.” Clearly, systems of insight are a type of advanced, centralized brain full of customer data that generates insights from that data. That’s certainly the type of functionality you want in your CDP.

The reality, though, is that to execute campaigns that engage audience members at a 1-to-1 level (and in real-time), a system of engagement must also act as a brain. It needs to leverage machine learning to sift through the vast amount of customer data and make the best decision about which experience, content, promotion, message or recommendation to deliver to each individual at any given moment (e.g., a person who just landed on your website, is opening your most recent email, is calling into your call center, etc.) and then deliver that experience…in milliseconds.

The only way to deliver true 1-to-1 experiences in real-time is to combine your personalization and customer data platform.

Here’s an Example

Let’s say you wanted to send an email to all the customers in your loyalty program. Your CDP would pass a segment of loyalty program customers to your ESP to do so. That’s pretty simple. 

But what if you wanted to personalize the email by featuring different creative based on each person’s favorite category? Then your CDP needs to pass several segments to your ESP (a segment of loyalty program members whose favorite category is women’s shoes, a segment of loyalty program members whose favorite category is men’s pants, etc.). 

And what if you wanted to tailor the content of the message even further to include different promotions depending on whether loyalty program members had visited your website in the last month? Then you’d need to create double the number of segments. You’d have one segment of loyalty program members whose favorite category was women’s shoes and who had been on the site in the last month, plus loyalty program members who have the same favorite category but who had not been to the site in the last month, etc.

It’s clear that managing all of these segments and mapping them to specific campaigns in your ESP can quickly get out of control.

However, if you use a CDP that can also activate the data directly, it doesn’t need to rely on segments passed between systems. It can analyze all of the data available within its own system and leverage machine-learning algorithms to select and present the most appropriate experience for each person. This is a much more scalable and personalized approach.

Final Thoughts

My colleague, Meera Murthy, VP of Strategy at Evergage, will be attending the upcoming Millenium Alliance Digital Retail Transformation Assembly on August 26-27 in Dallas, TX. If you’re interested in learning more about how Evergage can help you combine your CDP and personalization technology to deliver 1-to-1 personalization at scale, please schedule a strategy session onsite at the event.

ABOUT DIGITAL RETAIL TRANSFORMATION ASSEMBLY
C-Level experts from across North America’s retail industry are coming together in Dallas in August to anticipate the highly complex digital retail environment that will develop over the next few years.

Through a cutting-edge program designed by the industry, for the industry, we will provide a fresh and up-to-date insight to help move your organization to the next level of digital leadership. A series of executive education roundtables, keynote presentations, collaborative think tanks, educational workshops, and networking sessions will offer industry-specific topics and trends to ensure your company sustains its competitive advantage.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>

Round of Applause for Stefanie Strack, our Newest Keynote Speaker!

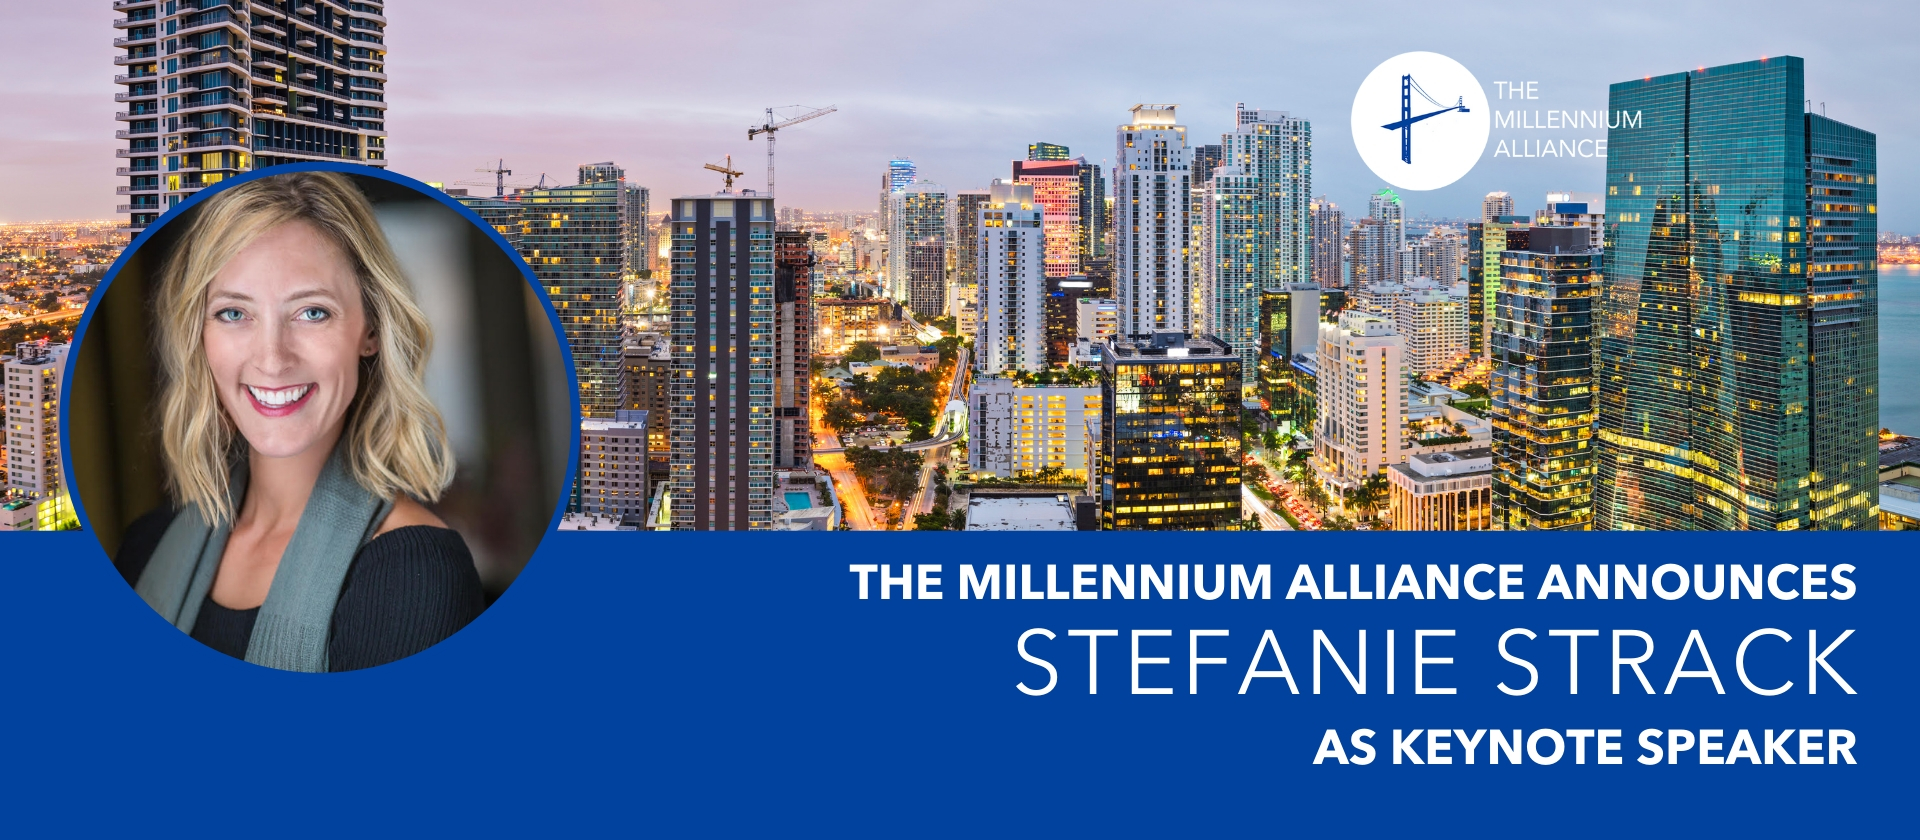
The Millennium Alliance is proud to announce Stefanie Strack, Founder & CEO of Voice in Sport and Former CEO of Rag & Bone, as the Keynote Speaker at our Transformational CMO East and Digital Retail Transformation East Assembly taking place on September 17 – 18th at The Mandarin Oriental in Miami, FL.

About Stefanie Strack:

Stefanie is an innovative executive with a passion to lead and inspire teams through transformational change. She has over 14 years of experience at Nike leading large scale corporate change across both small and large business units ($250M- $3.5B). Stefanie has a unique leadership background with experience across Merchandising, Product Creation, Sales, Strategy, Digital, Supply Chain and General Management.

In her last role at Nike, she created a new division called Express Lane which reimagined the way to serve consumers the most relevant product, at speed. Most recently she was the CEO of Rag & Bone in NYC. Today she is creating a new company focused on females in sport called Voice in Sport™ & VIS™.

Stefanie is living in Brooklyn NYC with her creative husband Alan Strack and two kids Siena (6) and Parker (3). She is originally from Alaska and played D1 soccer in college.

Digital Retail Transformation East

C-Level experts from across North America’s retail industry are coming together in Miami to anticipate the highly complex digital retail environment that will develop over the next few years.

Through a cutting-edge program designed by the industry, for the industry, we will provide a fresh and up-to-date insight to help move your organization to the next level of digital leadership. A series of executive education roundtables, keynote presentations, collaborative think tanks, educational workshops, and networking sessions will offer industry-specific topics and trends to ensure your company sustains its competitive advantage.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you a Retail Executive in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>

Welcome our Newest Keynote Speaker, Bob Evans!

The Millennium Alliance is proud to announce Bob Evans, Founder of Evans Strategic Communications and Former Chief Communications Officer at Oracle, as the Keynote Speaker at the Digital Enterprise Transformation and FSI Transformation Assembly taking place on November 13 – 14 at The Biltmore in Miami, FL.

About Bob Evans:

Bob Evans is one of the world’s leading analysts of the technology industry and the global phenomenon of digital transformation. In 2012, he was recruited by Oracle founder Larry Ellison to be the company’s first chief communications officer, and he left there after 5 years to launch the two businesses he runs today: Evans Strategic Communications LLC and Cloud Wars Media LLC. He’s given keynote talks about business innovation, digital transformation and customer-centric business on every continent on Earth (well, not Antarctica), and his daily analyses of the enterprise-technology market can be found on his media-company website at CloudWars.co.

Digital Enterprise Transformation Assembly

As more and more businesses look to digital technology and strategies to transform their business, CIOs know that data and information technology have never been more important. Understanding the convergence of mobile, social, and cloud is the first critical step for organizations looking to create opportunities and stay ahead of the competition.

The Millennium Alliance is thrilled to present our bi-annual Digital Enterprise Transformation Assembly, put together by the industry, for the industry. Join us in Miami, FL. for a series of executive education roundtables, keynote presentations, collaborative think tanks, educational workshops, and networking sessions will offer industry-specific topics and trends to ensure your company maintains its competitive advantage.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>


Does a $5B Fine Change Anything for Facebook?

The past 2 years have been trying times for Facebook- In February of 2018, German and Belgian courts ruled that the company broke data privacy laws for failing to ask users permission before collecting data for advertising purposes. March 2018 brought us the Cambridge Analytica scandal, releasing that 87 million users had their data acquired by the British political consulting firm, Cambridge Analytica, for commercial use. November exposed Facebook’s racial discrimination issues and December found a flaw in security that allowed app developers to have access to users’ unpublished photos. 2019 has Facebook in and out of court, and now they’re facing a $5B fine from the FTC. The $5B fine is unprecedented, actually, it’s 20x’s greater than the largest privacy/data security penalty ever exposed, but many call to question whether the levy renders any consequences for the tech giant.

Upon the approval of the FTC’s $5B fine, stock prices jumped 1.8%, and Q2 generated $15B in revenue with $3B of that being set aside for the anticipated fines. That being said, $5B is somewhat of an arbitrary amount of money for Facebook, and the settlement holds no one liable for Facebook’s privacy violations – meaning Mark Zuckerberg holds 0 responsibility for the repeated offenses.

Something needs to change, but can we truly rely on Facebook to create, implement, and maintain better privacy policies for the long term? The FTC is requiring Facebook’s transparency on consumers’ public and private data usage with third parties, as well as more extensive security and maintenance of user data, but Zuckerberg himself has expressed the desire for the government to have a more direct role in internet privacy regulation. We’ve repeatedly seen the same problem occur again and again under the watchful eye of the FTC, and the scale of the scandals have only grown. For the time being, we can only hope that Facebook’s bad press in the public eye is an incentive for major structural change, especially given that a historic, billion-dollar fine isn’t enough to shake their stock price.

Transformational CISO

The Millennium Alliance is thrilled to present our bi-annual Transformational CISO Assembly, taking place in Nashville, TN.

With the instances of cyber attacks increasing, businesses of all sizes are working tirelessly to secure their networks, devices, and data. Fortune 500 organizations are especially vulnerable as they have big data pools and thousands of people who need access. CISOs need to plan for worst-case scenarios, stay ahead of the latest IT Security transformation technology, and maintain their company’s information assets, all without losing sight of the corporate culture.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you a CISO interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>

Introducing our Newest Keynote Speaker, Ben Rhodes!

The Millennium Alliance is proud to announce Ben Rhodes, Author & Former Deputy National Security Advisor, as the Keynote Speaker at the Transformational CISO Assembly taking place from November 19-20 at The Hutton Hotel in Nashville, TN.

About Ben Rhodes:

Ben Rhodes is the author of the New York Times bestseller The World As It Is; a contributor for NBC News, MSNBC and Crooked Media; the co-chair of National Security Action; and an advisor to former President Barack Obama. From 2009-2017, Rhodes served as a Deputy National Security Advisor to President Obama. In that capacity, he participated in nearly all of President Obama’s key decisions, and oversaw the President’s national security communications, speechwriting, public diplomacy and global engagement programming. He also led the secret negotiations with the Cuban government which resulted in the effort to normalize relations between the United States and Cuba, and supported the negotiations to conclude the Joint Comprehensive Plan of Action (JCPOA) with Iran. Prior to joining the Administration, he was a Senior Speechwriter and foreign policy advisor to the Obama campaign. From 2002-2007, he worked for former Congressman Lee Hamilton, supporting his work on the 9/11 Commission and Iraq Study Group. A native New Yorker, Mr. Rhodes has a B.A. from Rice University and an M.F.A from New York University.

Transformational CISO Assembly

The Millennium Alliance is thrilled to present our bi-annual Transformational CISO Assembly, taking place in Nashville, TN.

With the instances of cyber attacks increasing, businesses of all sizes are working tirelessly to secure their networks, devices, and data. Fortune 500 organizations are especially vulnerable as they have big data pools and thousands of people who need access. CISOs need to plan for worst-case scenarios, stay ahead of the latest IT Security transformation technology, and maintain their company’s information assets, all without losing sight of the corporate culture.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you a CISO interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>

Security Newsletter: Edition 3

Battling the InfoSec Talent Shortage: 3 Tips for Hiring Security Staff

“The infosec talent shortage!” “There’s too many roles and not enough candidates!” So many excuses get thrown around about why security teams can’t find talent. Let’s cut to the chase – yes, hiring is hard and there are reports of more jobs than candidates. However, many of the reasons a team can’t find talent is due to the approach used for security hiring. There are actually many tricks and techniques that can help your team-building approach.

Let’s explore 3 changes that can dramatically increase your ability to hire great security folks

#1 Get rid of the security unicorn job description

#2 The fallacy of certifications and degrees

#3 Look internally – growing security members from within your company

#1 Get Rid of the Security Unicorn Job Description

How often do you see a job description like this:  “Junior security analyst needed. Must be expert in red team and forensics. Previous experience leading organizations through ISO27001 certification. Previous coding experience required.”

Wow, let’s unpack that. We just defined a junior level analyst role, tacked on expertise in two different domains (red team and forensics), then asked for experience in a totally different domain, ISO certification experience. And, to top it off, threw in another entire profession at the end – software development. Sure, it’s farcical and exaggerated, but it’s really not that far from the truth of many job postings. This brings us to the first tip for growing your security team – take a hard look at your job descriptions.

A critical activity before attempting to grow your team is to have a clearly defined job description. This sounds like boring HR driven requirements, but it really is crucial for hiring security talent. It’s important to step back and look at the core skill areas and the level of expertise needed in each domain. For example, while at Twitter I lead this exercise when growing our application security team. Here are the core skills we were looking for:

  • Application security testing
  • Secure code analysis
  • Secure software architecture design
  • Ability to develop security solutions
  • Developer security training

During interviews, we would find candidates great in security testing and code review, but poor in their ability to develop security solutions or vice versa. As we dug in, we realized we were searching for the unicorn. After weighing the different areas we discovered that we actually needed two different roles – an application security consultant to help drive the secure SDLC and review and also and a developer-focused security engineer to build reusable software in the name of security. As we broke this up into two unique roles we also weighted the importance of the different core skills and communicated this to the interviewing team. We don’t need the world’s leading expert in every category. Familiarity in some areas is appropriate, whereas expertise in other areas is a must for the role. The important item was to define these needs, document them, and communicate to the interviewing team. Now, with a clear definition of skills and levels of expertise, we were able to find great candidates for both roles.

#2 The fallacy of certificates and even degrees

A certification is great for learning, but it’s horrible as a screening mechanism for hiring. I get why people hate the job descriptions that ask for X certification. I agree, it’s a bad and lazy approach to hiring. But don’t blame the recruiters, they are taking the lead (or lack thereof) from the security hiring managers.

Instead, hiring managers have to work with the sourcers and recruiters to identify skills, experiences and potential previous roles that indicate a good potential candidate. Talk with you sourcer and describe the role and previous experience that would be relevant. Also talk about other similar roles that aren’t a fit since that will likely come up. I’ve also found it very helpful to take it a step further and craft a few specific screening questions recruiters can ask candidates during their initial call. These can be relatively basic questions, but the important thing is to create buckets of potential answers – ‘great’, ‘good’, ‘not a fit’. This way the recruiter can do an initial screening to see if candidates are a good match to begin the interview process.

Here’s an example:

“Tell me a few considerations for secure password storage within a web application”

  • Great answers – they talk about ‘pbkdf2’ or ‘bcrypt’. The candidate possibly mentions that these only protect against offline attacks against the hash so online attacks must be considered via brute force protection. May touch on other related concerns like password reuse attacks.
  • Good answers – mentions using a good hashing algorithm and a unique salt
  • ‘Not a fit’ – Generically mentions to just “use encryption” or to store it in a database and be sure no one can access it without any other details

As you can see, we’re not going into great depth with a single question. But if you’re hiring for an application security role a reasonable candidate for a non-entry level role should easily respond in a way to be bucketed into good or great – and hence move forward to the hiring manager. Also, just the activity of having a security person explain a security topic to a non-security co-worker is a great test. If that is a difficult experience for the candidate then you may not want them to represent the security team interacting with others in your company.

#3 Growing security members from within your company

Hiring is both a science and an art and while good interviewing may identify talented individuals, there still is the unknown element whether the individual will be successful at the company. However, if you “hire” individuals from within the company you have an incredible advantage, they already have a track record of success (or not, in which case you should tread carefully).

But how do you hire a person that isn’t in the security team into a security role? Don’t think of security as an entire discipline from top to bottom, but rather a specialization on top of an existing base skill. Here are a few security roles and base skills:

  • Application security engineer – software developer
  • Enterprise/Corporate security engineer – SRE, IT, or DevOps
  • Security risk management – compliance, internal audit, risk

Suddenly, you’ll notice you have a large pool of individuals more than qualified in the foundational skills for your role. In addition, they already know the ins-and-outs of how the company and tech stack operate. Plus, since they’ve worked at the company for some amount of time you’ll have real references on their performance. With this foundational knowledge, you have a great indication if this could be a solid employee in the security team. You’ll still have to conduct parts of the interview process, and see if they’re really up for the new style of work, but you’re starting from a great spot!

Security is in high demand but you can build and grow great teams

Hiring great security team members may seem challenging. And rightfully so, because it is. But if you reflect on your hiring process, criteria, and where you’re looking for candidates, you’ll be able to increase your chances of success. But just remember, hiring a great security individual is just the first step – you also have to set them up for success and grow their skills and career. But that’s a topic for another day.

Michael
Want to chat? Find me @_mwc

Understanding the FaceApp Frenzy

FaceApp is a free smartphone app that uses AI technology to apply age-enhancing filters to users’ photos, but we’re sure that you’re already aware at this point. The viral app sparked an overnight craze on social media with celebrities Drake, The Jonas Brothers, Lebron James, Gordon Ramsey and countless others sharing their refined new looks.

Just as fast as the social trend caught on, the Russian-based tech firm that developed FaceApp began to face massive public scrutiny with concerns over data privacy. Widespread panic began to escalate once cybersecurity experts raised red flags over the Terms and Conditions of the app, namely the parts that require access to all photos and “perpetual, irrevocable, nonexclusive, royalty-free (and) worldwide” license to use your photos, name, and likeness. The collection of user data isn’t out-of-the-ordinary, but the public’s reaction to FaceApp’s policies speaks volumes to the growing distrust in tech companies Post-Snowden, WikiLeaks and Cambridge-Analytica.

The Washington Post reported that photos accessible to FaceApp were stored on ordinary, American-run servers and the company has no known ties to the Russian government. It’s also been revealed that most images are removed from their servers within 48 hours. Even so, the FTC and FBI have been called to further investigate and reduce the risk of data misuse.

 “Nothing in life is free.”

On Twitter, Facebook, Instagram, or any website or app devoid of a pay-wall, you’re paying with a currency far more valuable than the dollar, your data. With cybersecurity and data privacy increasingly becoming a concern in the public eye, it’s important that cybersecurity experts acknowledge the fine-print. For those in the industry, these policies are somewhat commonplace, but the outcry that FaceApp recently created is proof of the disconnect between what users are willing to provide, and what they’re actually giving up.

Transformational CISO West

We’re thrilled that you’re interested in Transformational CISO West Coast in August 2019.

With the instances of cyber attacks increasing, businesses of all sizes are working tirelessly to secure their networks, devices, and data. Fortune 500 organizations are especially vulnerable as they have big data pools and thousands of people who need access. CISOs need to plan for worst-case scenarios, stay ahead of the latest IT Security transformation technology, and maintain their company’s information assets, all without losing sight of the corporate culture.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>
Marketers: Prove Your Cause

Social cause marketing, without a doubt, is the leading trend in marketing right now. During Pride month this year, it became evident that every brand under the sun had a Pride campaign – we noticed Bud Light, Listerine, Kind Bar, Smirnoff, Verizon, J.Crew, Nike, Playboy, and even the Donald Trump’s webstore had something rainbow to offer. Although social cause marketing is a great way to engage an audience and tie-in purpose into your brand’s messaging, consumers are quick on the trigger when it comes to calling out bandwagoners (lest we forget Pepsi’s 2017 Kendall Jenner commercial). With 2 out of 5 Pride campaigns donating no profits to the LGBTQ+ community, consumers are skeptical to say the least. Sure, Gen Z is twice as likely than any other group to have an interest in issues of equality, but they’re also more likely to not trust businesses to act in the interest of society, according to MarketingDive.

Honesty can be your best marketing strategy.

Companies like Lush Cosmetics have long prevailed their mission for ethical and environmentally-conscious sourcing, and the proof is in the pudding – a number of their products donate 100% of proceeds to a social cause and their owned media shows audiences the “behind the scenes” of how, where, and who are sourcing the ingredients in their products. In stride of their environmental efforts, they’ve launched packaging-free product lines and even 100% packaging-free stores in the UK.

Lush is a prime example of social cause marketing done right. Brands shouldn’t hop on any and every popularized social cause, but rather, their company’s ethos and mission should become part of the brand’s story in every aspect, whether launching a product, sharing on social media or building out a marketing campaign. In Gary Vaynerchuk’s words, “The best marketing strategy ever: CARE.”

Next on Millennium Live:

Globally-recognized marketer and best-selling author, Mark Schaefer.


Transformational CMO East

The digital revolution has forever changed the balance of power between individual consumers and brands. This need to think “customer first” has made the marketing function more vital than ever before.

C-Level executives around the world are anticipating that digital technology will continue to drive business. We’ve put together a series of executive education roundtables, keynote presentations, collaborative think tanks, educational workshops, and networking sessions with our industry experts and advisory board.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you a CMO interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>
Is the Drive-thru the Final Frontier for AI?

AI is so prevalent in our everyday lives – I wake up in the morning and ask Alexa about the weather, open Google Maps on the way to a meeting and find the fastest route into the city, Gmail offers a handful of reply suggestions to my emails using Smart Reply and now, all Tesla cars have full self-driving hardware. AI technology has simplified nearly every aspect of our day in and day out, but for some reason, ordering a burger at the drive-thru is just as cumbersome as it was 7 decades ago.

5thru Technology is hoping to change that process – with their drive-thru accelerator technology, restaurants are able to use license plate recognition for customer profiles and automated pre-pay while you’re still waiting in line (so you’ll never need to take out your wallet and stretch out to the window ever again). Line time is cut down by 55% using their system, and it even has the ability to up-sell customers with AI-based recommendations using historic data on a customer’s past orders.

5thru’s founder, Daniel McCann, told CIODive, “Drive-thrus are one of those things that are still being done today as they were 50 years ago… it’s largely ignored the new technologies that are available today. I think it’s ripe for an overhaul to bring it into the 21st Century.”

The drive-thru accounts for nearly 70% of fast-food sales, but the convenience and technology behind them have remained stagnant with line times growing as a result. There are countless opportunities to collect data when ordering from a drive-thru; restaurants could build customer profiles, implement intuitive recommendations and aggregated consumer insights at the hyper-localized or regional level for data-driven menu selections.

The 21st century has made our mornings, commutes, workdays, and leisure times so much smarter and more intuitive, and if self-driving cars are pulling up to McDonald’s in the near future, it’s about time the drive-thru was brought into 2019 through data collection and machine learning for a better customer experience.

Digital Marketing Transformation

With 53% of Marketers planning on adopting Artificial Intelligence in the next 2 years, the digital marketing revolution is just getting started. CMOs and CDOs alike are seeking new ways to maximize their digital reach to attract new business to, as well as deliver enriched, personalized experiences to existing customers.

The Digital Marketing Transformation Assembly will bring together North America’s most prominent digital marketing technology and business leaders from all major consumer-driven industries to discuss the latest technology, innovations, and strategies driving digital marketing in 2019 and beyond.

Are you interested in becoming a sponsor for this event? Click here today to learn more >>

Are you interested in attending this event? Inquire here today to find out if you qualify for Millennium Membership >>
Security Newsletter: Edition 2

A periodic newsletter from me, Michael Coates, on building security programs, security career growth, and emerging trends. If you were forwarded this newsletter, you can sign up here to receive updates.

The “Untrusted” Internal Network – Now What?

For years it has been an “us” vs “them” mindset in security. The bad folks are somewhere in the world – name a current adversarial country or organization – and our company is filled with good people. Therefore, if we build a big barrier around our company we can keep out the bad and everything is good, right?

The “crunchy perimeter & squishy center” security model has come and gone – at least it should be gone. It’s a relic of an old time and has no place in today’s modern enterprise defense. For those of you that may be fortunate to have avoided it, what is this model? Here’s the quick info. The idea was to build a strict and highly regulated perimeter around the company. Firewalls blocked almost all traffic in and out. Any exceptions were strictly reviewed and scrutinized. Laptops either didn’t leave the office at all or maybe had a forced VPN to tunnel all traffic back through the office network. While the perimeter was strong, once inside there was a more relaxed environment of trust. Because, hey, we can trust all of our employees, right? (in general, sure, as a global policy, definitely not)

What happened to this model? My argument isn’t that we should dissolve the perimeter or cast those efforts as worthless. Instead, we must accept that the paradigm has shifted. There is no longer a formal boundary between outside and inside or “us” and “them”. The rise of cloud computing, SaaS applications, continued connectivity to business partners, contract workforces, BYOD and more all mean that the “internal” network is a very busy place with many different people, systems, and notably – many threats.


Two Big Reasons to Ditch the “Strong Perimeter & Squishy Center” Mentality

First, insider attacks are a real concern and not just a theoretical exercise. Insider attacks may be the result of malice or just carelessness, but there is no denying that they are happening. The 2019 Verizon Data Breach Report shows that in some sectors “Privilege Misuse and Error by insider account for 30 percent of breaches”. Multiple articles also show how prominent tech companies have felt the impact of overzealous employees abusing their access to private data.

Second, even if we assume there are no malicious insiders, the “squishy center” mentality means that once inside the network, an adversary has free rein. Taking this one step farther, we’re essentially saying that if an attacker ever finds a vulnerability in the perimeter then the breach is not just a perimeter breach, but likely a massive breach of internal systems and data too!


We agree, the internal network is untrusted. Now what?

Although the internal network may not be trusted, this doesn’t mean we throw out the firewalls and just let it be a free-for-all. Instead, let’s double down on the concept of least privilege, which the perimeter is the first step to broadly eliminate access to the world unless they authenticate via VPN. The next logical step is applying least privilege inside the network. In other words, shift the mentality in all places to enforce strong authentication, access control, and minimal access policies. One way to think about this is that the company network is essentially a coffee house wireless network. No trust is implicitly granted just because a person is in a particular physical location and has internet access. Instead, trust is proved whenever access to systems and data is required.

Here are a few concrete steps to help move a company in this direction

  1. Company Education – Wide company awareness and support is required. Teams building internal systems for sales, data science, developer efficiency etc all must understand that authentication and access control is required – even though the systems are internal only. As a security team you’ll be viewed much more favorably if you also provide pre-vetted libraries to achieve auth’n and auth’z.
  2. Security Architecture & Strategy – It’s time to understand and plan for a migration to a Zero Trust security model. Don’t be overwhelmed by hype here, you don’t need to do a full scale overhaul. But there are many small steps you can take to incorporate Zero Trust concepts into your security posture.
  3. Data First Security Policy – We’ve established that access to an internal network does not imply trust, therefore we must evaluate how trust is established for access to internal data systems. As a security exercise, look at two internal data stores, one within your on prem data center and one within a cloud deployment. Evaluate how you authenticate and authorize services or users that can access the data. For the services, follow the call chain. How do you ensure that the individual initializing the services call is authenticated and authorized for the action. This gets tricky, but it also gets to the core of a data first security policy. Without confidence in these controls you are instead relying on only trusted actors on your internal network – which we know is no longer realistic.

The migration from a long held security approach and belief system may be challenging. You’ll undoubtedly have naysayers and others that believe this work is paranoid and unwarranted. In all areas of security it’s critical to return to fundamental risk modeling practices. If your company is moving forward to adopt new technology architectures and business relationships, then your threat model is evolving too. Through your risk management you either accept the new risk, hold back the business by denying technologies or update mitigating controls to safely enable the business. The only thing I hope you don’t do is cling to old truths that no longer hold – unless verified by your fresh risk evaluation specific to your company’s profile, risk model and controls.

Michael
Want to chat? Find me @_mwc